The Hack You Never Clicked: Why Cyberattacks Are Becoming Inevitable
by Brian Pollack
I feel like it's inevitable that I will get hacked. Citizen Lab just proved spyware can arrive through an online ad without a single click.
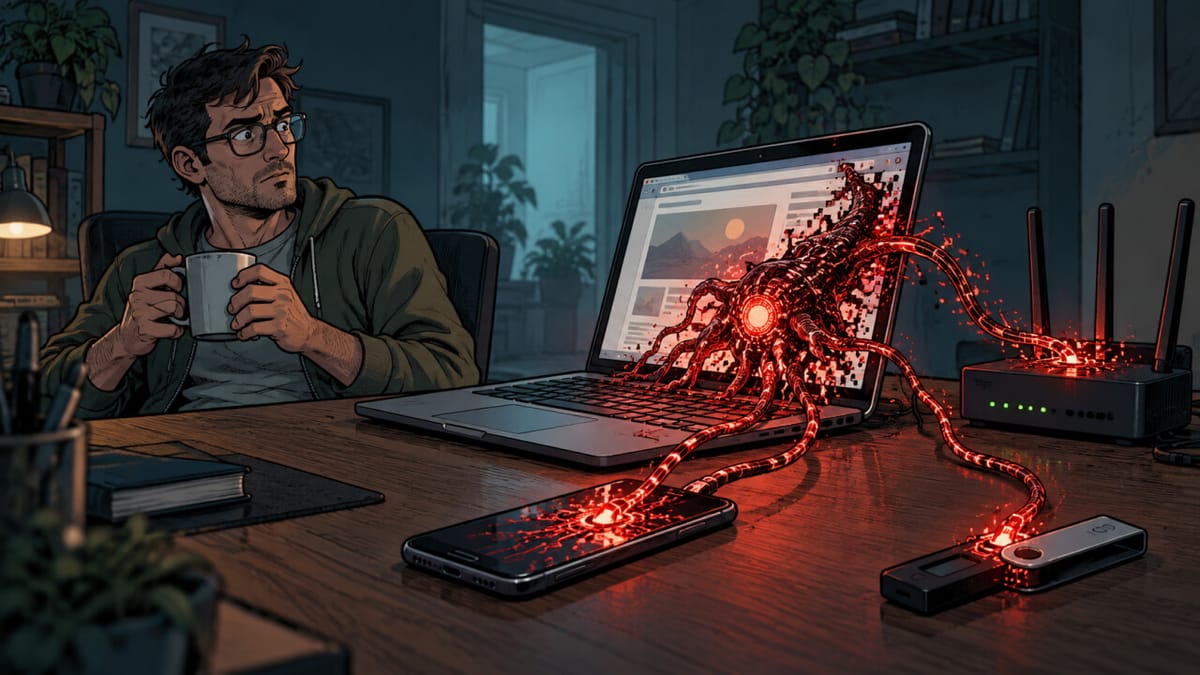
An Israeli company posing as an ad firm let spyware vendors aim ads at specific people. At least 45 computers at Al Jazeera were infected, and the ads ran across tens of thousands of apps and websites. That means any site or app that shows ads could deliver spyware, and you don't have to do anything at all. Right now this is expensive spyware sold to governments and aimed at specific people, but it could be any of us at any time.
This is very much like a new disease. If it infects a few people, it's very hard to isolate and defend against. If they spread the hack wide, it would get caught, analyzed, and blocked faster. Even then, millions could be infected before patches were released in a well-coordinated attack.
When Trusted Hardware Turns Against You
Ledger, a popular hardware crypto wallet, just confirmed that wallets sold through one reseller in Malaysia had a hidden cellular chip added inside. That parasite watched the screen, captured the recovery phrase, and sent it out over the cell network. The thieves then drained the wallets in a way that is impossible to reverse and far too late to stop. The tampered wallets were selling for nearly half price.
Hackers have also been quietly installing bandwidth-sharing software on D-Link storage drives, old Ubiquiti video recorders, and other devices so they can resell your home and office internet connection. In March the FBI said one proxy service had sold access to about 369,000 hacked devices, mostly home and office routers. It's only a matter of time before people are getting takedown notices for torrents they aren't hosting, spam they aren't writing, or hack attempts they aren't making. How long before Grandma is getting raided for unthinkable downloads she knows nothing about because the router her grandson set up 4 years ago hasn't been updated?
Preparing for the Inevitable
Bank of America says it brought in 1,000 contractors to patch software flaws found by Anthropic's Mythos AI. How many companies can afford 1,000 extra people? More importantly, how many are willing to spend that much (or anything) on non-capitalized overhead?
Make sure you update your devices. Spend the extra money on quality hardware from manufacturers that ship security patches quickly, and replace anything they've stopped supporting. Citizen Lab rightfully suggests installing an ad blocker and turning off ad tracking. Use a privacy-focused browser such as Brave, Zen, LibreWolf or Brave and Safari on Mobile.
If you run a company or an IT department, schedule a call with me. Let me get some experienced human eyes on your code to see what your exposure is. We can do code reviews, set up secure zones, isolation paths, secure mobile devices, and put plans in place just in case the unlikely turns inevitable.
An earlier version of this article was published on LinkedIn by Brian Pollack. This edition has been expanded and edited for the Protovate blog.
Originally published on Protovate.AI
Protovate builds practical AI-powered software for complex, real-world environments. Led by Brian Pollack and a global team with more than 30 years of experience, Protovate helps organizations innovate responsibly, improve efficiency, and turn emerging technology into solutions that deliver measurable impact.
Over the decades, the Protovate team has worked with organizations including NASA, Johnson & Johnson, Microsoft, Walmart, Covidien, Singtel, LG, Yahoo, and Lowe’s.
About the Author